Project · Mobile device management

Tether

Every phone, enrolled, configured and accounted for.

An Intune / Jamf-style MDM for company and BYOD phones, tablets and laptops — QR enrollment, configuration profiles, compliance, realtime remote commands including Lost Mode, and coordinated rollouts.

Open live demo Source: private repo
Role
Solo · Design & full-stack
Type
Mobile device management
Stack
Next.js · Supabase
Status
● Live demo
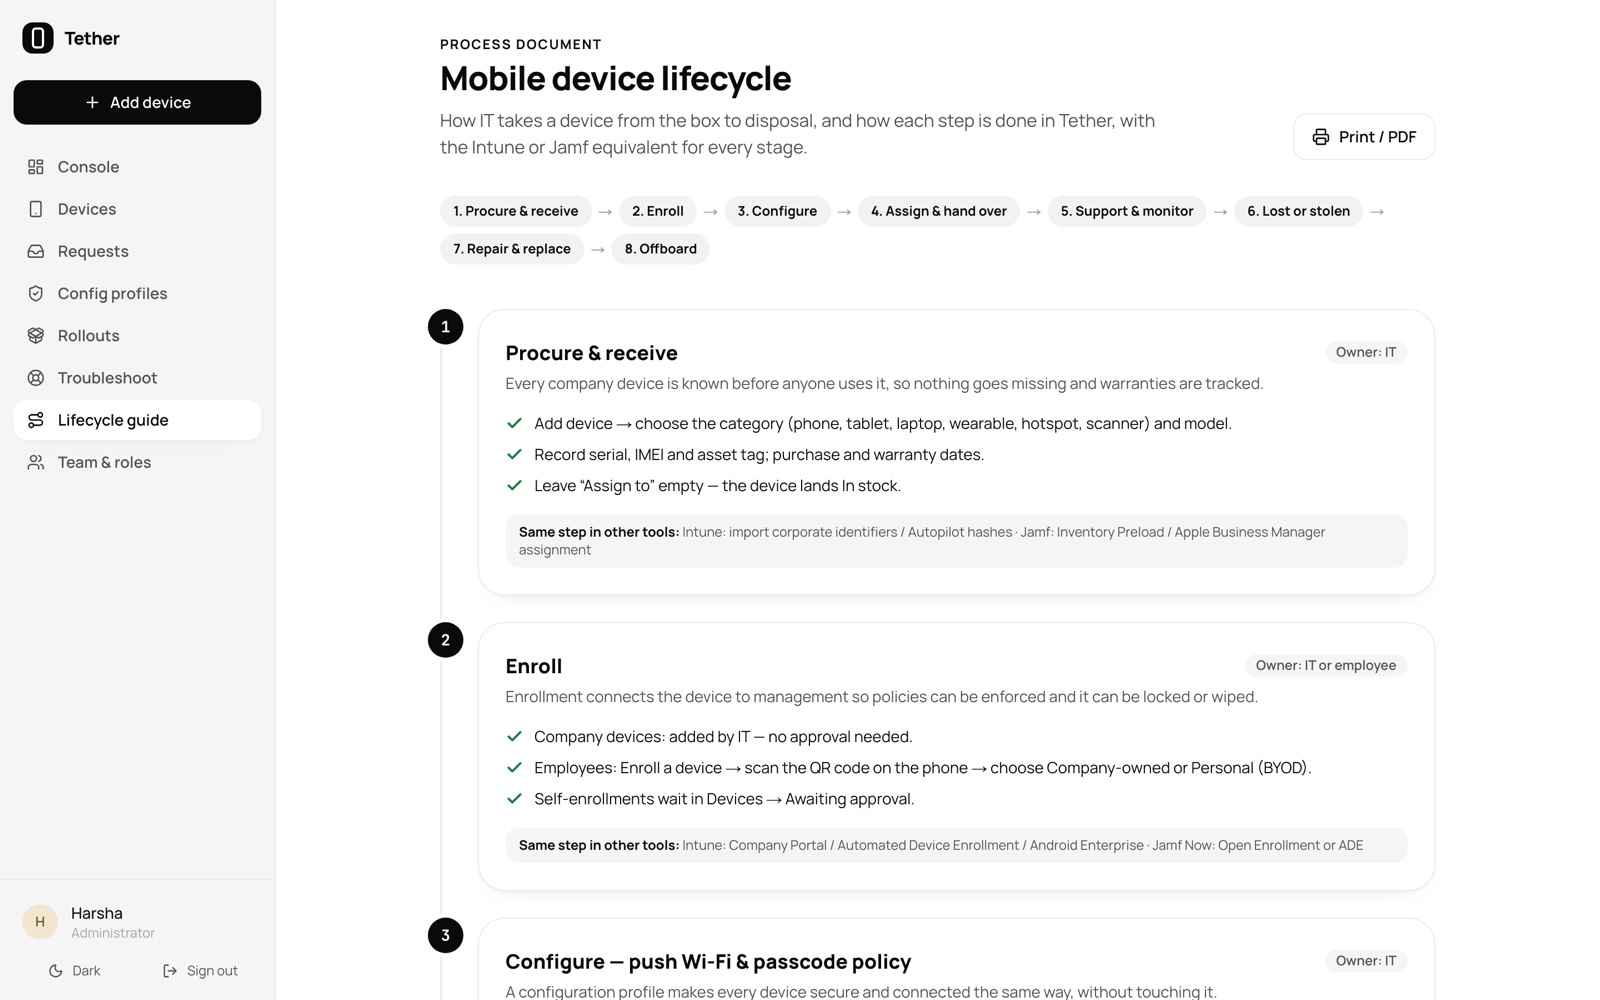
Mobile device lifecycle guide with Intune / Jamf equivalents

// Mobile device lifecycle guide with Intune / Jamf equivalents · demo accounts available on request

The problem → the approach

The problem

Phones are the hardest endpoints to support: mixed ownership, privacy expectations on personal devices, constant sync issues, and no way to act fast when one goes missing.

The approach

Tether covers the whole mobile lifecycle — enroll by QR, push a profile, show users platform-specific compliance fixes, troubleshoot sync with guided wizards, and lock a lost device instantly.

What it does

QR enrollment

Employees scan a code; the phone identifies itself and walks through ownership and privacy in plain language.

Configuration profiles

Passcode, Wi-Fi, VPN, email and required apps as versioned profiles pushed to devices.

Lost Mode & remote commands

Queued commands with delivery acknowledgement — Lost Mode locks the phone in realtime; wipes need type-to-confirm.

Compliance with fix steps

Each failure comes with steps for iPhone, Android, Mac or Windows so users fix it themselves.

Sync troubleshooting

Decision-tree wizards for email, calendar and contacts sync with an escalation summary.

Rollouts

A 5-stage board tracks a team refresh from allocation to the old device being returned and wiped.

Screens

// Configuration profiles
// Mobility console
// Troubleshooting wizards
// Sign-in

Who uses it

Employee
Company Portal, enroll a device, requests, troubleshooting
Technician
Console, devices, approvals, profiles, rollouts, requests
Admin
Everything above plus deletes and team & roles

Security, enforced in the database

Row-Level Security on every table — calling the API directly returns exactly what the screen shows, nothing more.
Writes go through role-checked SECURITY DEFINER functions that verify the caller before changing anything.
61 automated checks (scripts/e2e.mjs) cover row-level security, role-checked functions and remote-command guard rails.
No secrets in the client or the repository — only the public Supabase URL and anon key, protected by RLS.
61
automated security checks
6
device categories
7
configuration profiles

Tech stack

Next.js 15TypeScriptTailwind CSS v4Framer MotionRechartsqrcodeSupabasePostgres RLSRealtime

What's next

Real MDM integration (Apple MDM, Android Enterprise, Intune Graph)On-device agentWeb PushCarrier & plan trackingConditional access